Thailand internet café data rules were the subject of an August 2008 Personal Thailand warning. It told readers that internet operators would have to keep traffic data and identify users, raising questions about privacy in an era of shared computers.
The 2008 change as it was reported
The original post said a requirement affecting internet cafés and other organisations would take effect on 23 August 2008. A contemporaneous Kasikorn Research Center note described a one-year grace period ending on that date and a requirement for covered organisations to retain logs with user identification for at least 90 days.
That contemporary account supports the broad historical point, although the original blog’s detailed claims about every website visited and every type of organisation should not be treated as independently established by it.
What a traffic log is — and what this article does not claim
Traffic records concern connections and use of a system. They are not automatically the same thing as a complete record of every message a person writes. What is retained depends on the applicable legal instrument and the service.
The original also asserted broad criminal consequences for visiting particular categories of sites. Those claims need their own legal analysis and have not been carried forward here. Nor does the 2008 article settle how any present-day business must configure its systems.
A record of changing internet habits
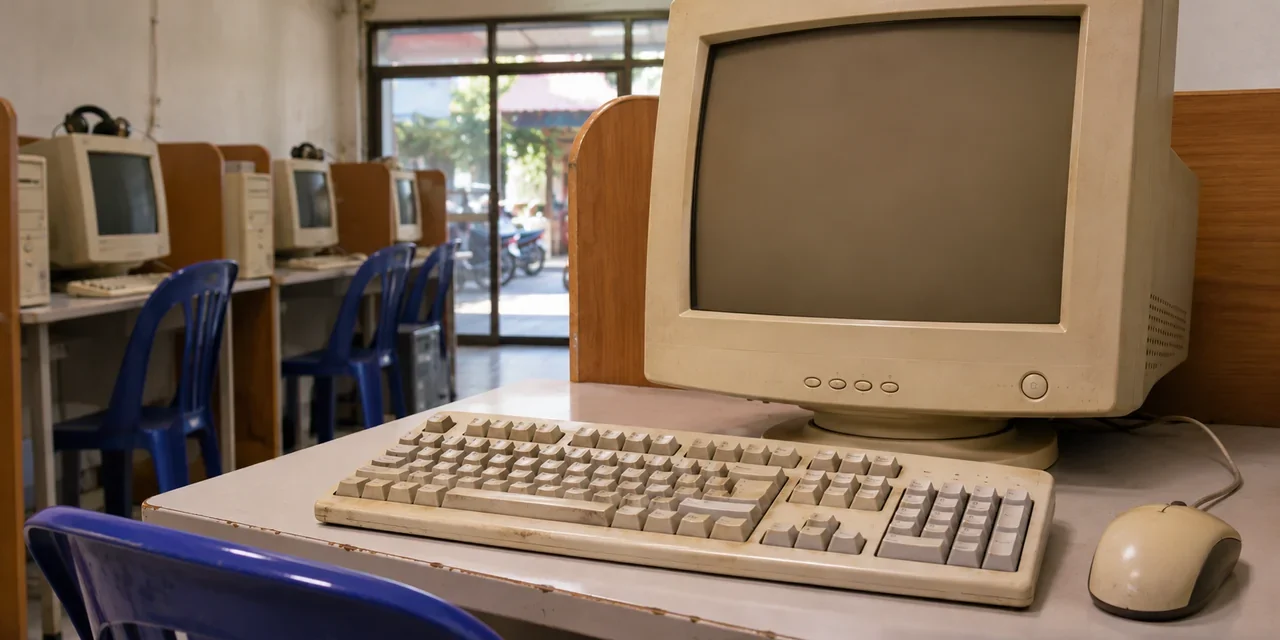
In 2008, shared computers in cafés and hotels were an ordinary way for travellers to communicate. A rule about identifying users therefore affected both operators and people stopping in to use a machine.
The UN Office on Drugs and Crime hosts a later English rendering of section 26 of the Computer Crime Act that describes retention duties for service providers. It is useful background, but this historical article does not attempt to give a complete account of later amendments or today’s obligations.
Related reading: Thailand’s changing mobile internet.
FAQ
What date did the historical report focus on?
It focused on 23 August 2008, when a contemporaneous account said a grace period ended.
What period did the 2008 account discuss?
The contemporary research note described retention for at least 90 days for covered organisations.
Does a traffic log necessarily contain every message?
No. Traffic data should not automatically be treated as the complete content of every message.
Is this a compliance guide for operators today?
No. It describes the 2008 report; operators should check current requirements with the relevant Thai authority.
More from Personal Thailand
If you enjoy practical reporting and personal perspectives on Thailand, you can support my work and explore member-only content through either platform:
- Subscribe to Personal Thailand on X — creator membership with access to applicable subscriber-only posts and benefits.
- Join or support Personal Thailand on Buy Me a Coffee — browse available memberships and support options.
These are separate services with different charges and membership benefits. Paid access may be required; subscribing on one does not automatically grant access on the other. The main information in this article is free to read above.